Security & Multi-Tenancy
Serve many customers from one platform, with strict separation between them.
Designed for managed service providers
Three layers of tenant isolation
Every query is filtered by the caller’s tenants, composite foreign keys block cross-tenant references, and PostgreSQL row-level security enforces isolation in the database itself.
Sign in your way
Microsoft Entra ID (multi-tenant) or local accounts for your staff, with Argon2 password hashing, failed-login lockout and per-address rate limiting. Your customers can sign in with their own company account, see below.
Two-factor sign-in
Authenticator-app codes with one-time recovery codes for local accounts, and a switch to require them for all staff. Entra ID sign-in inherits your Conditional Access policies.
Sign-in activity
The collector reads the sign-in logs of your Linux devices, routers and access points, and the Windows Security log, and keeps only counts. You are warned when a sign-in service is being guessed at from the internet, when failures spike, and, most seriously, when a sign-in succeeds from an address that had just been failing. Account names tried by attackers and log lines never leave the device.
Five roles
MSP admin, technician admin, technician user (view-only), customer admin and customer user.
Encrypted credentials
Device credentials are encrypted and never returned to the browser. Collectors authenticate with their own long-lived credentials.
Audit log
Every administrative action, sign-in and failed sign-in is recorded with where it came from. The log can be exported and shown to be untouched, see below.
Backups you can restore
Nightly database backups, plus password-locked full backups you can download. Send copies off the server to S3-compatible storage, Azure Blob or an SMB share, and restore a whole platform from the installer on a new machine.
Undo a configuration mistake
TechSavve keeps snapshots of its own setup: monitors, maintenance windows, business services, automatic fixes, notification choices, the on-call roster, report schedules, patch policies and more, taken automatically when something has changed and whenever you ask. Compare one with today and roll back everything, chosen parts or one customer. A rollback can itself be undone, and secrets are never part of a snapshot.
Consent before remote support
A support link shows the customer who is asking before anything runs, and records their agreement.
Your data stays with you
TechSavve runs on your own server. Customer data, credentials and logs never leave your infrastructure.
Your branding
Operator logo and branding throughout the portal.
Customer single sign-on New
Let a customer’s people sign in to their portal with the account they already use at work: Microsoft Entra ID, Okta, Google Workspace, Auth0, Keycloak, ADFS, or anything that speaks OpenID Connect or SAML 2.0.
One provider per customer
Each customer has its own provider and its own e-mail domains. You can set it up, or a customer’s administrator can do it themselves, in which case a DNS record must first prove that they own the domain.
People appear when they sign in
The first sign-in creates the account. Groups in the provider decide the role and the sites someone can see, and you can refuse anyone whose group is not mapped.
Offboarding takes effect
Turn someone off at the company and they can no longer get in: SCIM switches the account off, password sign-in can be blocked, and a session renews for no more than eight hours after the company sign-in.
Strict about the sign-in itself
Tokens and SAML assertions must be correctly signed, issued to this platform, unexpired and answer a request this platform made. Staff accounts and other customers’ accounts are never linked to a customer’s provider.
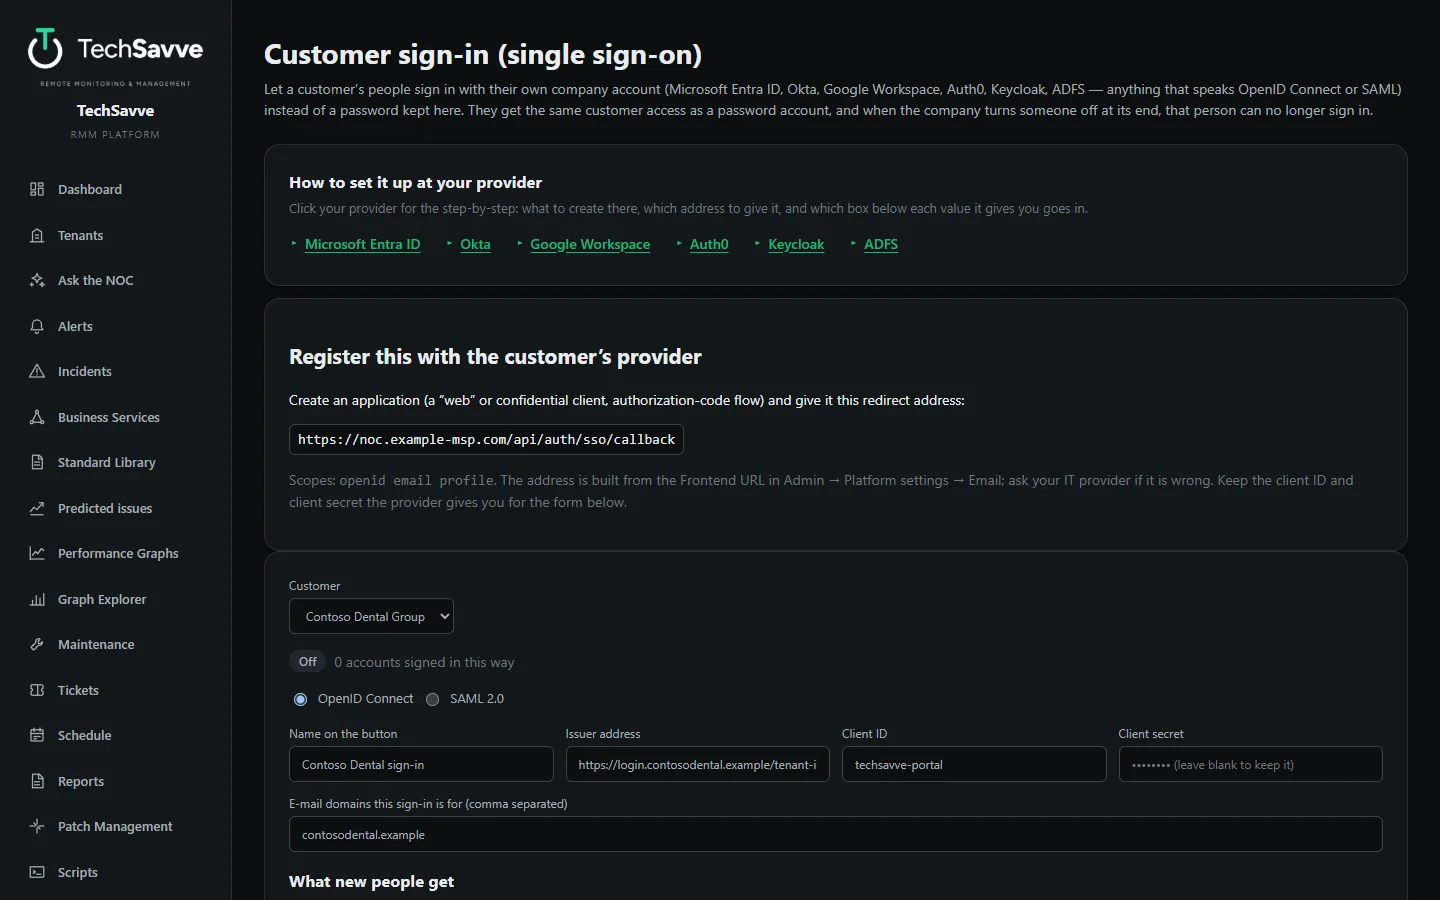
New. Tested against simulated identity providers, which refuse forged, expired and replayed sign-ins, but not yet against a customer’s real Entra ID, Okta, Google or SAML provider. We would set up the first one with you.
An audit trail you can prove New
For the day an auditor, an insurer or a customer asks what happened and who did it.
Everything, with where it came from
Administrative actions, sign-ins and failed sign-ins (with the reason, never the password), the address each came from, and the history of tickets and incidents, in one view you can filter by person, action, customer and date.
Export it
CSV, JSON or NDJSON with a SHA-256 fingerprint, or on a schedule: each export holds what the last one did not, is compressed with a manifest, can be e-mailed to your auditor and copied off the server.
Tamper-evident
Every entry is sealed into a chain with a key kept only on the server. Editing, removing or reordering entries in the database breaks the seal, and a daily check says so. Keep a fingerprint elsewhere and removal at the end shows too.
Kept as long as you choose
Keep administrative entries for a number of days or for ever. The oldest are removed in order and a checkpoint records where the chain was cut.
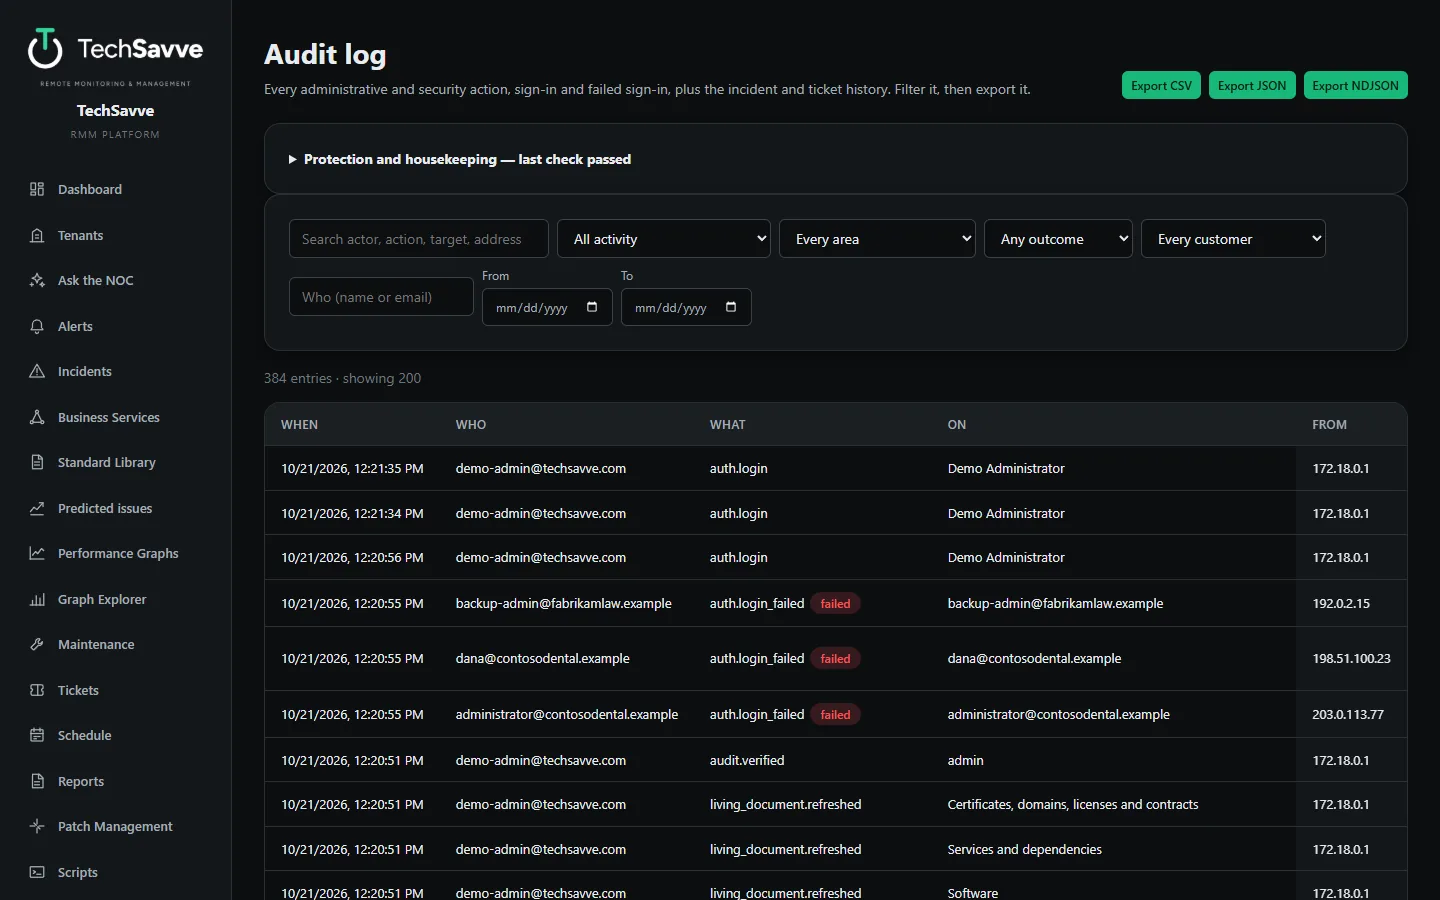
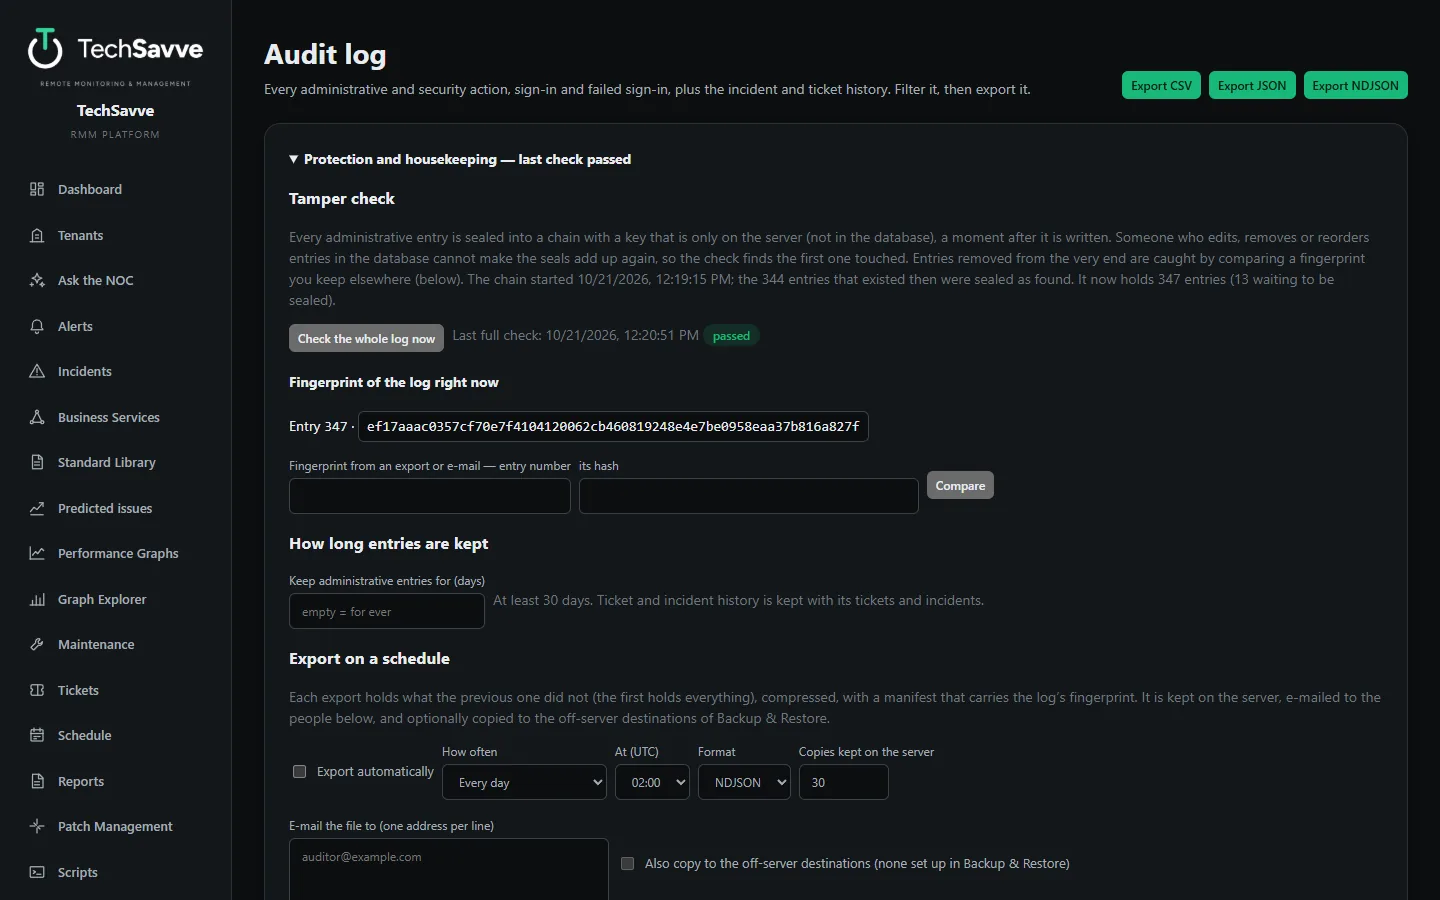
New. Verified with automated tests and on a test database, including a log someone has edited. Copies of exports to S3, Azure or SMB storage have not yet been run against a real storage account.
Send your logs to your SIEM New
TechSavve is not a SIEM and does not pretend to be one. It sends what it records to the one you already run, or to your customer’s.
What it sends
Seven streams, each switched on separately for a destination: administrator actions, incident history, ticket history, alerts opened, alerts resolved, internet exposure findings and sign-in activity.
Where it can go
Syslog over UDP, TCP or TLS as CEF or JSON, or HTTPS to a webhook or Splunk HTTP Event Collector with a bearer token or your own header. Step-by-step guides cover Elastic and Logstash, rsyslog, Graylog, Microsoft Sentinel, Splunk, Wazuh and a plain webhook.
One customer, one feed
A destination can be limited to chosen customers, so a customer’s own SIEM receives only that customer’s events.
Delivered, then caught up
Events usually arrive within a minute, each with a stable ID so a repeat can be dropped. After an outage it catches up from where it stopped, up to seven days back. A destination that keeps failing is marked failing and the audit trail records it.
New. Verified with automated tests, including real UDP, TCP and TLS servers, and on a test database. It has not yet been run against a live Splunk, Sentinel, Graylog or Wazuh; the guides follow those products’ own documentation.
Compliance packs New
For customers who have to show evidence: choose a framework for each customer, and TechSavve checks it every day, maps what it finds to the framework’s controls and exports the evidence.
Five frameworks
HIPAA Security Rule, CIS Controls IG1, GDPR Article 32, FTC Safeguards Rule and cyber-insurance requirements.
Checked every day
Encryption, patching, backups, two-factor sign-in, sign-in activity, what the network shows to the internet and more, from what TechSavve already collects plus a read-only scan of each device.
Attestations for the rest
Controls a computer cannot see, such as a risk analysis or a staff training record, are confirmed by a named person and stay valid for a year.
Evidence to hand over
A PDF and a ZIP with CSV and JSON for each customer, and their scores in the customer portal.
A compliance pack gathers technical evidence. It does not certify anyone, and each pack says so.
New. The daily device scan is newly released and has been tested on sample answers, not yet on a customer’s real fleet.
Microsoft 365 and Google Workspace New
Connect a customer’s Microsoft 365 or Google Workspace with read-only access, and TechSavve reads the things attackers look for.
Sign-in security
Administrators and users without MFA or 2-Step Verification, nothing requiring it, and too few or too many global administrators.
Mail risks
Inbox rules and forwarding that send mail outside the organization, the classic sign of a taken-over mailbox.
Licenses and mailboxes
Subscriptions expiring or suspended, paid licenses nobody uses, licensed accounts idle for months, and mailboxes or OneDrive nearly full.
Devices and alerts
Devices that are not compliant, a low Secure Score, and the provider’s own security alerts.
Fix it from here
Suspend a user and sign them out, reset a password, assign or remove a license, and change group members, with each action recorded.
New. The Microsoft 365 connection has run against real tenants. The Google Workspace connection has been tested against a simulated Google, not yet a customer’s real domain.
Endpoint security findings New
Connect CrowdStrike Falcon, Microsoft Defender for Endpoint or SentinelOne with read-only access, and the customer’s protection status sits beside everything else you watch.
Detections
Open detections by severity, so a critical one is an alert and a low one is a line on a list.
Protection gaps
Devices with protection off or only partly on, agents that have not reported for days or are out of date, and devices cut off from the network.
Coverage
Devices TechSavve sees on the network that have no agent at all.
New. The three connections were built against each vendor’s documented interface and tested with recorded answers. Tell us which one you use and we will confirm it before you commit.
A password vault for your team New
Passwords, notes and shared logins in a vault that runs next to TechSavve on your own server, built on open-source Vaultwarden. Not affiliated with Bitwarden, Inc.
One switch to turn it on
Admin → TechSavve PassVault turns it on or off from the web page, with no commands to run. A TechSavve PassVault link then appears in your team’s menu.
Invitation only
Nobody can sign themselves up and there are no password hints: an administrator invites each person.
In your branding
The vault wears the logos you upload for TechSavve, and TechSavve’s own when you have none.
Encrypted, and stays with you
Entries are encrypted before they leave the browser, and the vault’s data never leaves your server.
In every full backup
The vault is part of TechSavve’s full backups and restores with everything else.
Related guides
Self-hosted vs cloud RMM: what MSPs should weigh
Where your customers' data lives, who keeps the platform running, security, cost and network reach: the questions to answer before choosing a self-hosted or cloud RMM.
Agentless vs agent-based RMM: how they differ and when each fits
How agent-based and agentless RMM monitoring work, where each is stronger, the security trade-offs, and how to choose for your customers.
See TechSavve RMM in action
Book a free demo with the DFWTechPros team.