Network Visibility
See how each site is wired, who is using the bandwidth, and what the network devices are telling you.
A live map of every site
The Network Map draws each site from what TechSavve already knows: the collector, the switches, firewalls and hosts behind it, and the devices behind those. Problems are colored, big branches fold away, and you can show problems only or find a device in a moment.
- Built from the parent links you set and the VM-to-host links read from vCenter
- Set what a device is reached through right on the map
- A device behind a parent that is down shows as Unreachable and opens no incident of its own
- Refreshes itself every minute
Who is using the bandwidth
NetFlow and IPFIX
Point a router or firewall at the site collector (NetFlow v5 or v9, or IPFIX). The NetFlow page shows traffic in and out of each site, the busiest local and outside hosts, applications by port, and the top conversations.
Small enough to keep
Flows are summed into conversations on the collector, so only summaries travel and are kept: five-minute detail for two days, then hourly, for 30 days by default.
Bandwidth usage
Every interface on routers, switches, servers and PCs is counted hourly over SNMP, SSH or WinRM. See usage by day, month, quarter or year for each device and interface, on screen or as a scheduled report.
Listen to the network
SNMP traps
The collector receives SNMP traps (v1, v2c and informs) and matches each one to its device. Built-in rules turn UPS alarms into alerts, a UPS on battery is critical, and you can add your own rules for anything else.
Nothing missed
Every trap is kept for 30 days on its device’s page, repeats are folded together, and traps from senders TechSavve does not know yet are listed so you can add them.
Watched like everything else
Trap alerts go through the same incidents, tickets, on-call and maintenance windows as every other alert.
Know what is on the network New
A scan on a schedule finds what is new, what is reachable and what is risky, so an unknown device is a message to you and not a surprise during an audit.
Scheduled scans
The site collector sweeps a site hourly, daily or weekly, or on demand. Each device found keeps its open ports, name and fingerprint.
New devices raise an alert
The first run sets the baseline. After that a host nobody has seen before, and that is not already managed, raises a warning until you add it or dismiss it.
Risks worth fixing
Telnet and legacy remote services, databases open on the LAN, RDP, old SMB, VNC and FTP, printer and camera consoles, and SNMP with a default community, each with its own severity.
Default passwords, only if you ask
An optional check for printers and cameras tries a short, fixed list of published factory defaults over HTTP, makes only a few read-only requests per device, and reports a hit without doing anything with the access.
Findings say a service is reachable on the local network. Whether it is open to the internet is a separate question, answered by the internet exposure check below. The findings also count in the compliance packs and the business review.
New. Scheduled scans and the default-password check are newly released and have been tested against simulated devices, not yet on a customer’s network.
What the network shows to the internet New
A scan inside tells you what is reachable on the LAN. This asks the other question: what does the customer’s public address answer to anyone on the internet?
A plain connection check
The platform tries 64 well-known ports, such as Remote Desktop, file sharing, databases, VNC, SSH, management pages, cameras and printers, the way an attacker would. No passwords are tried. A web port gets one request for its front page, to name the product.
Only addresses you confirm
A named administrator confirms the address belongs to the customer, and who and when is kept. Private and reserved addresses are refused, a manual check cannot repeat within five minutes, and the address can be suggested from the collector’s own check-ins.
Severity, and an alert that clears itself
Remote Desktop or a database open to the world is critical, SSH and a NAS sign-in page are warnings, a web server is information. Critical and warning findings raise an alert that closes when the port does.
Into the paperwork
The result, with the findings from the network scans, feeds the HIPAA, CIS, GDPR, FTC and cyber-insurance packs and the quarterly business review.
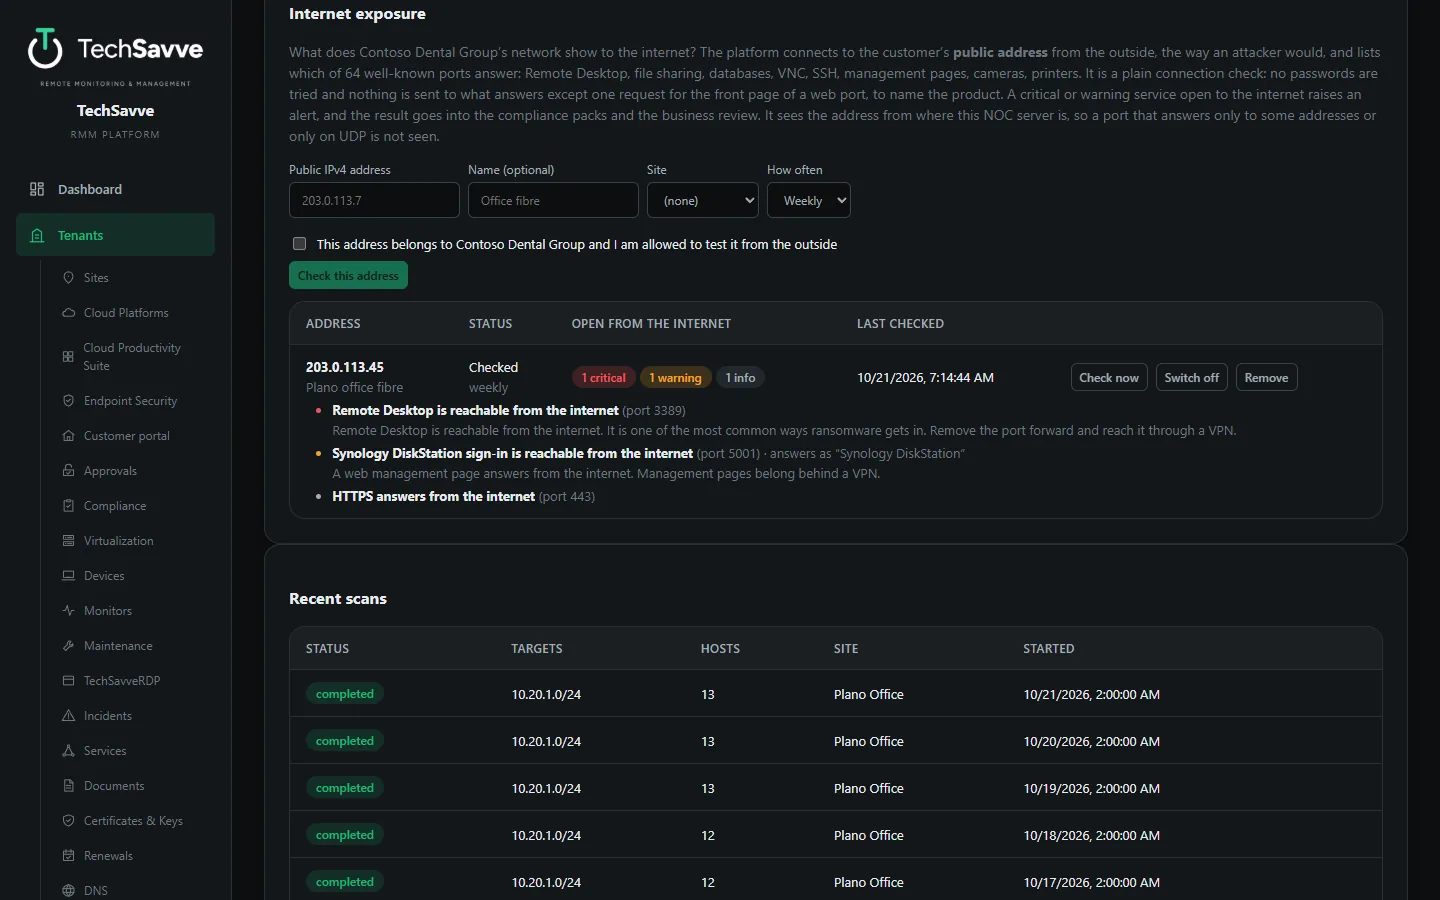
The check sees the address from where your TechSavve server is, over TCP only. A platform inside the customer’s own network sees that address from the inside, so the result says what it saw and from where.
New. Run for real against a test host that allows scanning, and tested with local sockets; not yet against a customer’s address.
See TechSavve RMM in action
Book a free demo with the DFWTechPros team.